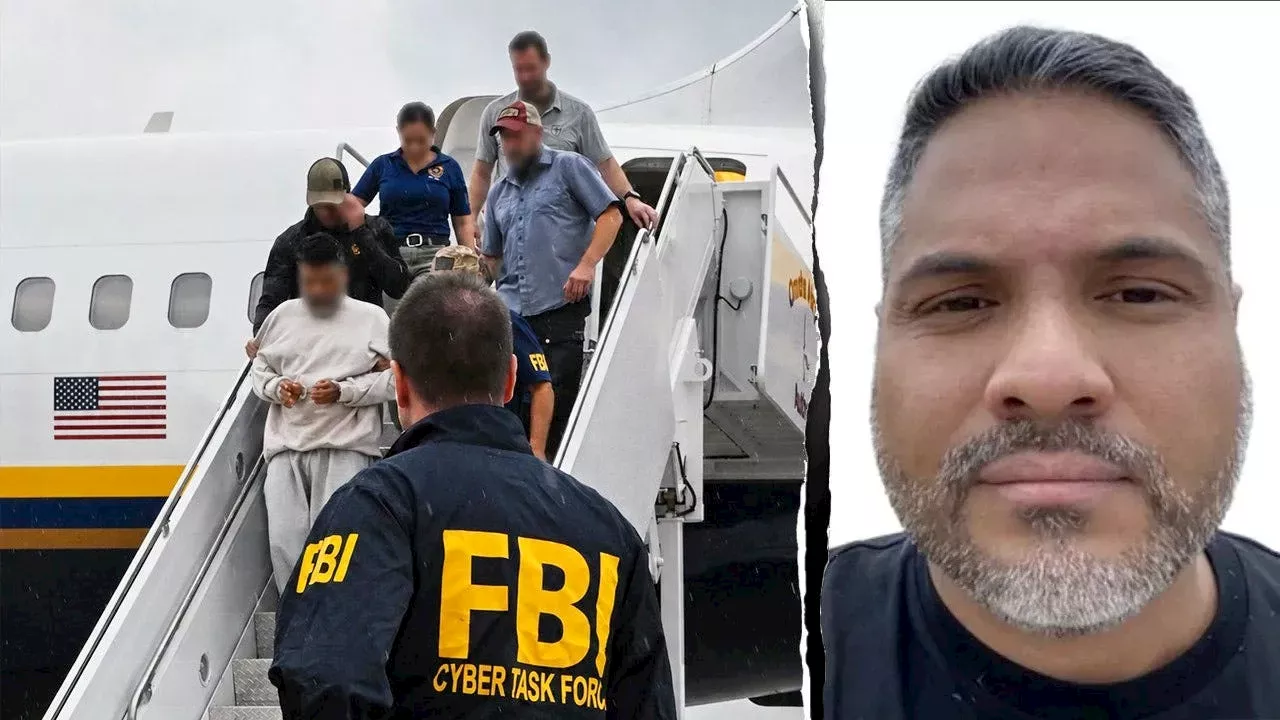
Anibal Alexander Canelon Aguirre, the first cybercriminal added to the FBI's Ten Most Wanted list, pleaded not guilty in a Nebraska court on Friday. After being apprehended in Venezuela, Aguirre faces four federal charges related to a massive ATM jackpotting operation.
The capture of the first cyber fugitive on the Ten Most Wanted list
The return of Anibal Alexander Canelon Aguirre to U.S. soil marks a significant milestone for the Federal Bureau of Investigation. According to Fox News Digital, FBI Director Kash Patel identified Aguirre as the first individual with a cyber-crime focus to ever be placed on the agency's Ten Most Wanted list. Patel highlighted that Aguirre's capture represents the 10th Most Wanted fugitive apprehended since the start of the Trump administration.
The FBI Director described the current agency as running on "supercharged horsepower," asserting that criminals can no longer find safe havens anywhere on the planet. This aggressive posture suggests a shift in how the FBI prioritizes digital fugitives, treating high-level hackers with the same urgency as violent terrorists or narcotics kingpins.
How ATM jackpotting funded the Tren de Aragua terrorist group
Anibal Alexander Canelon Aguirre, known by the aliases "Prometheus" and "The Engineer," is alleged to have led an international conspiracy to steal millions of dollars from financial institutions. As reported by the Department of Justice, these funds were used to support Tren de Aragua, a criminal organization that the United States has officially designated as a foreign terrorist organization.
The methodology used by Aguirre involved "ATM jackpotting," a sophisticated cyberattack where malware is used to exploit vulnerabilities in automated teller machines. This process forces the machines to dispense cash without authorization. The FBI told Fox News Digital that this specific scheme had been operational since at least 2024,providing a steady stream of illicit capital to the Tren de Aragua network.
Four federal conspiracy counts facing Anibal Aguirre in Nebraska
During his initial court appearance in Nebraska, the 50-year-old Aguirre pleaded not guilty to four distinct federal conspiracy charges. These counts include bank fraud and bank burglary, computer fraud,money laundering, and providing material support to terrorists.. The Department of Justice has confirmed that Aguirre will remain in detention in Nebraska while he awaits trial.
Todd Blanche, representing the enforcement effort, credited the success of the arrest to the Homeland Security Task Force and Joint Task Force Vulcan. Blanche stated that the objective remains to dismantle "narcoterrorist finance networks" and prosecute violent criminals to ensure the safety of American neighborhoods.
The missing details on the Venezuela-U.S. extradition process
While the report confirms that Anibal Alexander Canelon Aguirre was captured in Venezuela and returned to the U.S. last month, the specific mechanics of this transfer remain unverified. The source does not detail whether this was a formal extradition, a covert operation, or the result of a diplomatic agreement between the U.S. and the Venezuelan government.
Furthermore, it remains unclear if other members of the Tren de Aragua cyber-wing were apprehended alongside Aguirre or if he was targeted as a sole high-value asset. the current reporting focuses exclusively on Aguirre's legal status in Nebraska, leaving the broader scope of the Venezuelan operation unknown.
A shift toward targeting 'narcoterrorist finance networks' via cybercrime
The case of Anibal Alexander Canelon Aguirre reflects a broader global trend where traditional organized crime syndicates are adopting high-tech tools to fund their operations. By merging the violence of a group like Tren de Aragua with the anonymity of ATM jackpotting, these organizations have evolved into hybrid threats that require both digital forensics and traditional intelligence to dismantle.
This operation echoes previous U.S. efforts to choke off the financial lifelines of designated terrorist groups, but with a modern twist. The focus is no longer just on shell companies or drug trafficking, but on the exploitation of financial software and hardware vulnerabilities to generate liquid assets quickly.
Comments 0