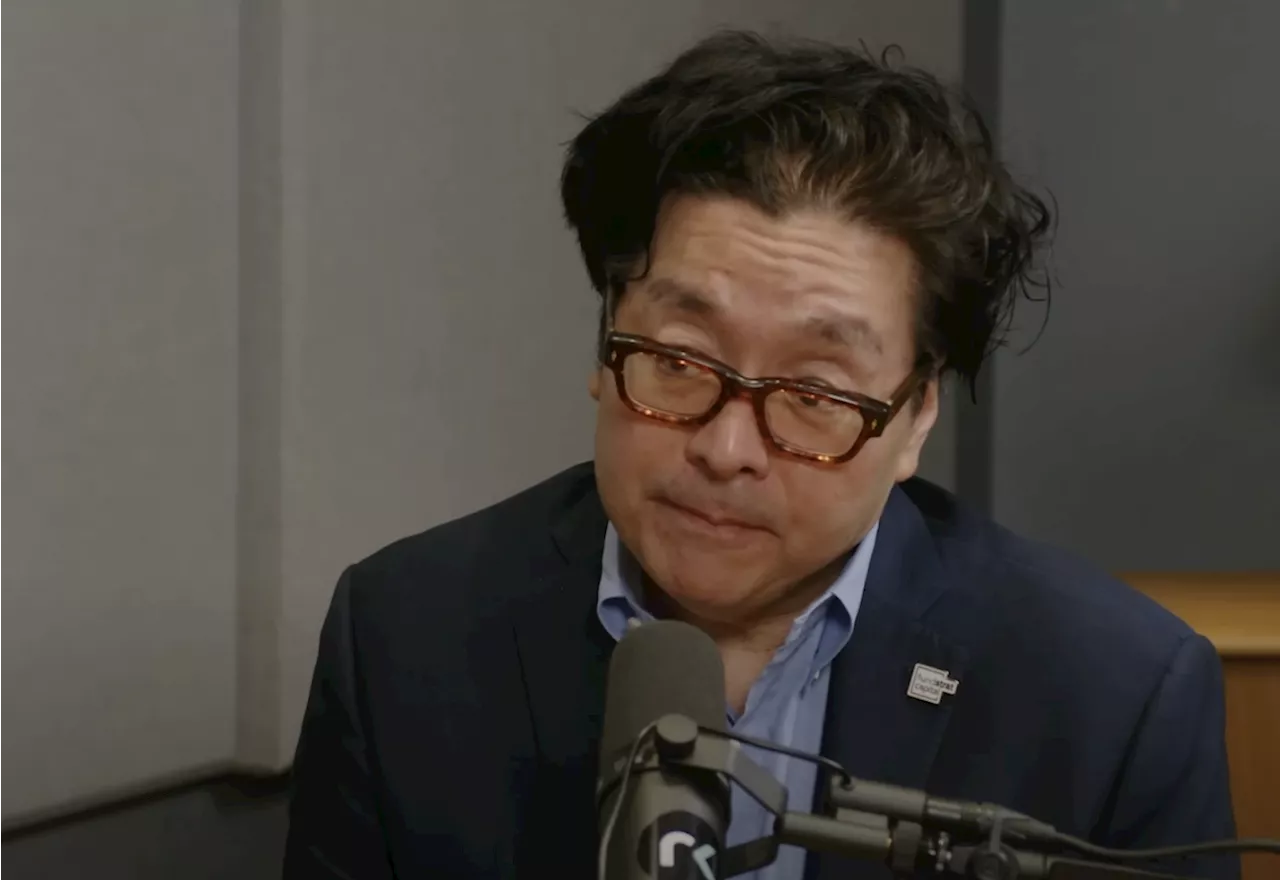
Fund manager Tom Lee warns that quantum computing could compromise Bitcoin's security by 2028. In response , Bitcoin advocate Adam Back argues that the network's cryptographic barriers remain robust against current quantum capabilities.
Tom Lee’s 2028 warning and the Shor’s algorithm threat
Fund manager Tom Lee suggests that Bitcoin faces an existential crisis as quantum computing technology matures. According to the report, Lee anticipates that the development of Shor’s algorithm will render existing cryptographic safeguards useless by the year 2028. This prediction, which draws on Google's research into post-quantum computing, has sparked significant speculation regarding whether the Bitcoin network can survive the coming decade.
The debate between Tom Lee and Adam Back mirrors the historical tension between traditional encryption and emerging quantum power.. As hardware capabilities accelerate, the question of whether current cryptographic standards can withstand the next generation of computing becomes a central concern for the entire cryptocurrency ecosystem.
Adam Back’s defense of ECDSA and seed phrase entropy
Bitcoin cypherpunk Adam Back argues that the threat posed by quantum machines is often overstated by critics. As reported by the source, Back points out that Bitcoin relies on the elliptic curve ECDSA standard for digital signatures rather than simple encryption for transaction validaiton. He emphasizes that the massive entropy found in seed phrases makes it virtually impossible for a quantum device to brute-force private keys.
The technical disagreement between Lee and Back centers on whether current quantum resources can actually overcome the complexity of Bitcoin's non-repeating public-private key pairs. While Lee views the arrival of quantum-capable machines as a looming deadline, Back maintains that the cryptographic barrier remains a formidable obstacle for any quantum computer attempting to crack the ECDSA standard.
The 7 million Bitcoin sitting in vulnerable legacy addresses
A significant portion of the Bitcoin supply remains at risk due to the way certain addresses were historically managed . The report highlights that approximately 7 million BTC—roughly 35% of the total supply—reside in legacy addresses where public keys have been exposed through address reuse . A sufficiently powerful quantum computer could theoretically use Shor’s algorithm to derive private keys from these specific exposed points.
The vulnerability regarding legacy addresses raises critical questions about the fate of lost or dormant coins. It remains unverified whteher the owners of these 7 million bitcoins, including those believed to belong to Satoshi Nakamoto, will ever be able or willing to migrate to new, quantum-secure addresses. Additionally, the community has not yet reached a consensus on how to handle these funds without triggering massive market volatility or accidental loss.
Dilithium, Falcon, and the controversy of the BIP-361 freeze
Protocol designers are already researching post-quantum signature schemes like Dilithium and Falcon to prepare for future network upgrades. Implementing these changes would likely require a significant hard-fork to replace the existing ECDSA mechanism across the entire network. However, coordinating such an upgrade among a global, decentralized group of node operators presents a massive logistical and social challenge.
The BIP-361 proposal suggests locking exposed coins for a limited period to prevent them from being stolen by quantum attackers.. This proposal is highly controversial because it could effectively freeze a third of the total Bitcoin supply, potentially alienating long-term holders and impacting the asset's overall liquidity. Proactive development remains essential as the field of quantum hardware continues to evolve rapidly.
Comments 0